How Do Manufacturers Provision Devices with wantasticd genkey?
Generate one stable device identity in the factory, print a safe customer claim QR, and let first boot complete enrollment without exposing the private key.
Praxisnahe Beiträge zu MikroTik-Fernzugriff, OpenWrt-Agenten, WireGuard-Mesh-Design und Gerätemanagement-Automatisierung.

Generate one stable device identity in the factory, print a safe customer claim QR, and let first boot complete enrollment without exposing the private key.

Run the portal, WireGuard core, Postgres, Redis, nginx, certificates, and firewall in one container, then connect your first device.

Choose interactive, token, or manual enrollment, install the agent as a native service, and verify the device in the Wantastic console.

Enroll a wantasticd endpoint, confirm its WUSP model, inspect fleet health, and apply supported device changes over the authenticated overlay.

Connect RouterOS with native WireGuard, create a managed Winbox account, and give technicians access without exposing TCP 8291 to the internet.

Create a browser-based SSH session to a connected endpoint without a public SSH port, a local VPN client, or shared fleet credentials.

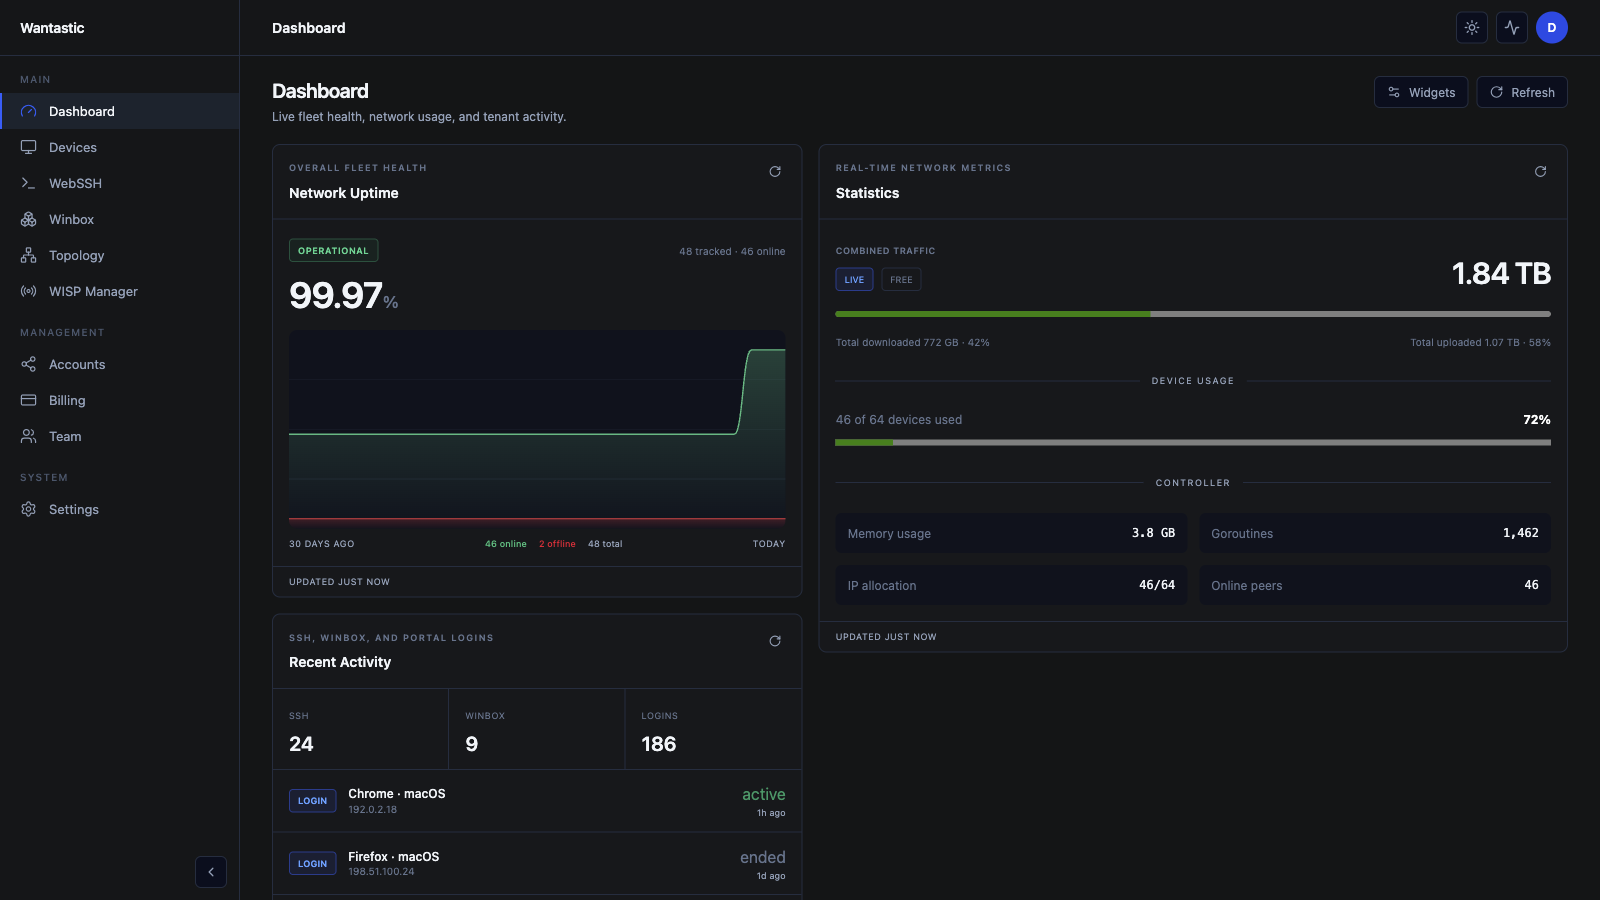
Use the live dashboard to triage fleet health, understand traffic and capacity, inspect recent access, and decide which device view to open next.